Don't stress over your website's policies: we explain it simply
Your website's privacy policy, terms and conditions and cookies sound like boring fine print, until one slip-up costs you dearly. Here we explain, simply and without legal jargon, what each one is, so you can stop stressing and keep your website up to date.
By Jonathan Arocha
I’ll be honest with you from the start: when I began working with websites, I wasn’t entirely clear on what privacy policies, terms and conditions, cookies and all those things you accept without reading actually were. They sounded like fine print, like boring paperwork, like something only lawyers care about.
Later I understood that ignoring them can be expensive. Very expensive. And if it happened to me, it surely happens to a lot of people who have, or want to have, a website. So this article is here to explain it to you simply, without beating around the bush, the way I wish someone had explained it to me.
First things first: are they all the same thing?
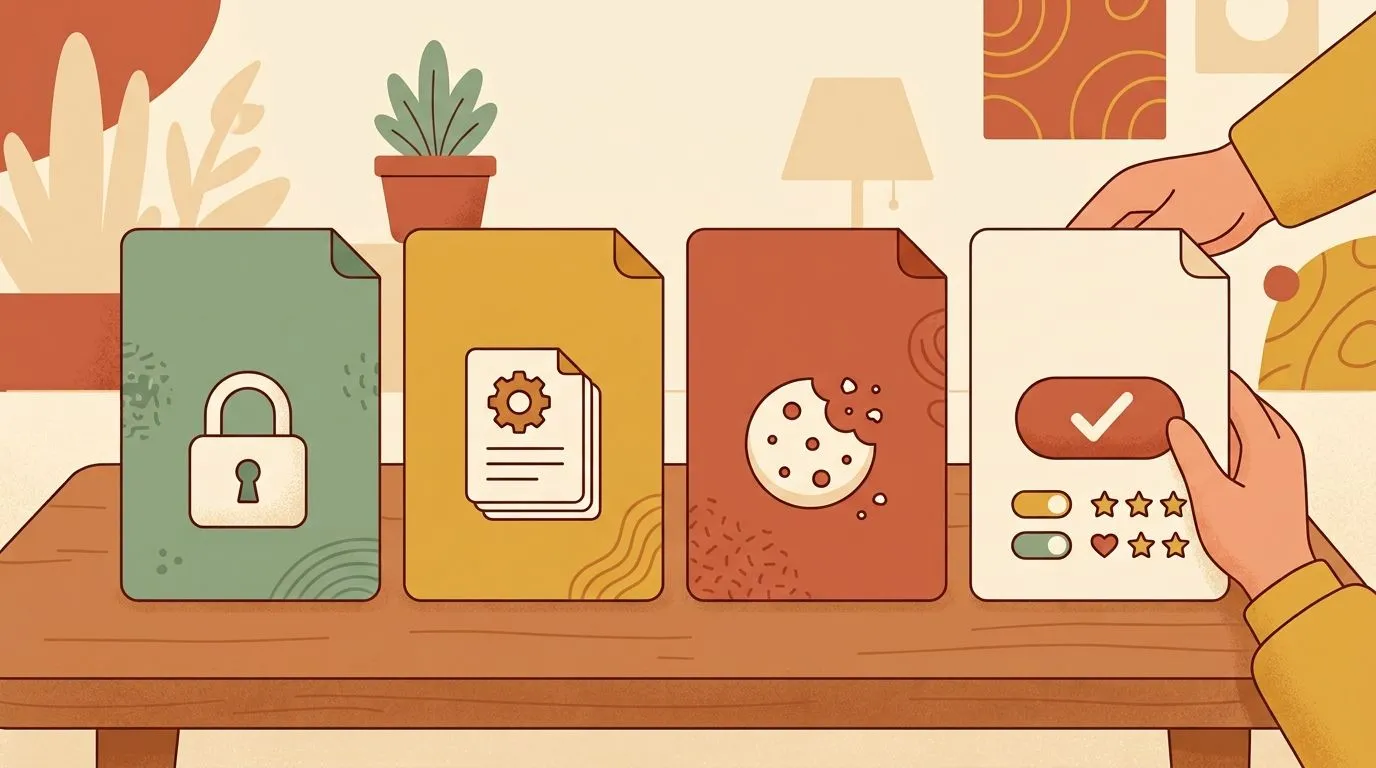
No. And that’s the first confusion worth clearing up, because a lot of people think “the policies” are a single document, when in reality they’re four different things that do different jobs.
The privacy policy is, in a nutshell, “this is what I do with your information.” It explains what data you collect from the people who visit your website (their name, their email, their phone number, even browsing data), what you use it for and who you share it with. It’s the document the law requires of you in almost every case, because almost any website collects some data, even if it’s only through a contact form or analytics tools.
The terms and conditions are something else: they’re the rules of your site. What can and can’t be done, how a purchase works, returns, payments, how far your liability goes. If the privacy policy mainly protects the visitor, the terms mainly protect you.
The cookie policy is smaller and more specific. It only talks about cookies, which are those trackers that store information about how people use your website. It’s like a chapter within the bigger topic of privacy.
And finally there’s the consent banner, which isn’t a document but that little window that pops up asking your permission to use cookies. Its job is to capture your “yes” or your “no” before the trackers are activated. The document explains; the banner asks.
And are they always the same for everyone? Not that either. And here comes a costly mistake: copying another website’s policy and pasting it into yours. It doesn’t work, because the content changes depending on what data you collect, what marketing tools you use and what countries the people who visit you are from. An online store’s policy looks nothing like a blog’s.
And why should I care about all this?
This is where you’re probably thinking, “well, sure, but nothing’s going to happen to me, I’m a small business.” I used to think the same. Let me tell you about something real.
In the United States there’s a clothing store called Todd Snyder. It’s not a giant; it’s a mid-sized business. For 40 days in 2023, the cookie banner on its website was misconfigured: it appeared and disappeared so fast that people couldn’t manage to reject tracking, even if they wanted to. It wasn’t done out of malice. It was a technical error, the kind anyone could make without noticing.
That error cost them a fine of 345,178 dollars.
Read that again: almost three hundred fifty thousand dollars, for a banner that didn’t work properly. Not for stealing data, not for lying, not for doing anything malicious. Just for having a tool set up wrong that they believed was working.
And it’s not an isolated or rare case. In California, lawsuits against websites over tracking issues went from about 200 in 2023 to almost 4,000 in 2024. Most of them target the same thing: sites that use tracking pixels or marketing tools without proper permission. Many of those lawsuits are aimed at small businesses, because they’re the ones that review these issues the least and the easiest to catch out.
I know this can make you a little anxious. That’s normal. But the good news is that protecting yourself from the basics isn’t that hard, and you don’t need to become a lawyer to do it.
The minimum you should have
Let’s get practical. To avoid the most common risks, these are the essentials:
If you have a blog or an informational website, you need at least a privacy policy and, if you use tracking or analytics cookies, a cookie notice with its banner. That covers the most important part, because almost any website collects some data.
If you also sell or take payments online, then the terms and conditions stop being optional and become essential, because that’s where you define the rules for purchases, payments, shipping and returns.
And a detail almost nobody takes care of: put the links to these documents in your website’s footer, so they can be seen from anywhere on the site. Don’t hide them.
When do I need a real lawyer?
Good news: most small businesses don’t need one to get started. Today there are tools that generate these documents for you by asking a few questions about your business, and for a simple case that’s usually enough.
But there are situations where a professional’s help is worth it. If you handle sensitive data (health information, financial data), if you collect data from minors, if you handle a very large volume of information, or if you operate in several countries at the same time, then your case is no longer simple and it’s worth having someone with legal judgment review it.
There’s a middle option that seems the smartest to me for a growing business: generate the documents with a tool and then pay a lawyer just to review them. It’s much cheaper than drafting them from scratch, and it gives you peace of mind.
One last thing about this, and it’s important: policies aren’t “do them once and forget about it.” Laws change, technology changes, and your own business changes. It’s a good idea to review them at least once a year so they keep protecting you.
Where marketing and policies collide (and almost nobody sees it)
This is the point I most want you to take away, because it’s exactly where businesses get into trouble without realizing it.
The marketing tools you use every day (the Facebook pixel, Google Analytics, remarketing, ads) work by tracking people’s behavior. And here’s the trap: by default, many of those tools start tracking the moment someone lands on your website, before they’ve accepted anything.
That’s exactly what the law punishes. And the most important thing you need to know: the responsibility is yours, not Facebook’s or Google’s. You own the website, you installed the tool, you’re accountable.
The classic mistake is installing the Facebook pixel “and that’s it,” with nothing to hold it back until the visitor gives permission. That was, at its core, the same kind of mistake that cost much bigger companies millions. That’s why marketing and policies aren’t separate worlds: what your banner promises has to match what your tools actually do. If someone rejects marketing cookies, no pixel should fire. When those two things don’t match, that’s where the problem begins.
An honest clarification before I wrap up
Since this touches on legal topics, I have to be clear: nothing you’ve read here is legal advice. It’s a general explanation so you understand what it’s all about and stop feeling like it’s a language you don’t speak. For your specific case, especially if it’s one of the sensitive ones we mentioned, the right thing to do is always to consult a professional.
And there’s a golden rule that applies to any Hispanic business, wherever you are: what matters isn’t where you are, but where your customers are. Even if your business is in Mexico or Colombia, if you sell to or track people in the United States or Europe, those laws apply to you too. That’s why policies are adapted to each case and there’s no one-size-fits-all formula.
If you need help with this
I know it sounds like a lot. And it is, if you try to handle it alone. That’s why at BGC we do it for you.
If you already have a website and you’re not sure whether you’re covered, or if you want to launch one and do it right from the start, at Impulso Digital we make sure your site has what it needs to run with peace of mind. And if you just want to understand your situation better before deciding anything, we offer a free consultation to help you see where you stand.
You don’t have to become an expert in this. You just need someone who is, on your side.
You might also like
Does it make sense to write a blog in 2026 if everyone asks ChatGPT?
They say blogs are dead and that everyone now asks ChatGPT, but writing about your business is still one of the best decisions you can make. We explain why having a blog in the age of AI makes you a better communicator, and why that ends up influencing your sales.
Read articleHow to fill your salon with appointments using your website
Does your beauty salon already have a website, but it isn't filling your appointment book? Find out how to turn your site into a tool that books appointments online, makes you look more professional and works for your business every day.
Read articleHow a business creates value: the role of intangible assets
A company's value is almost never where you can see it: it lives in its intangible assets, its reputation, trust, knowledge. This post opens a column on how that value is created, protected and exchanged. Told by someone who practices the craft every day and is still learning it.
Read article